
Vraxum finds the vulnerabilities in your code.
An agentic code security scanner. It maps your codebase as a graph, lets an AI agent reason over it, and reports each finding with its evidence and, where it can, a proposed fix.
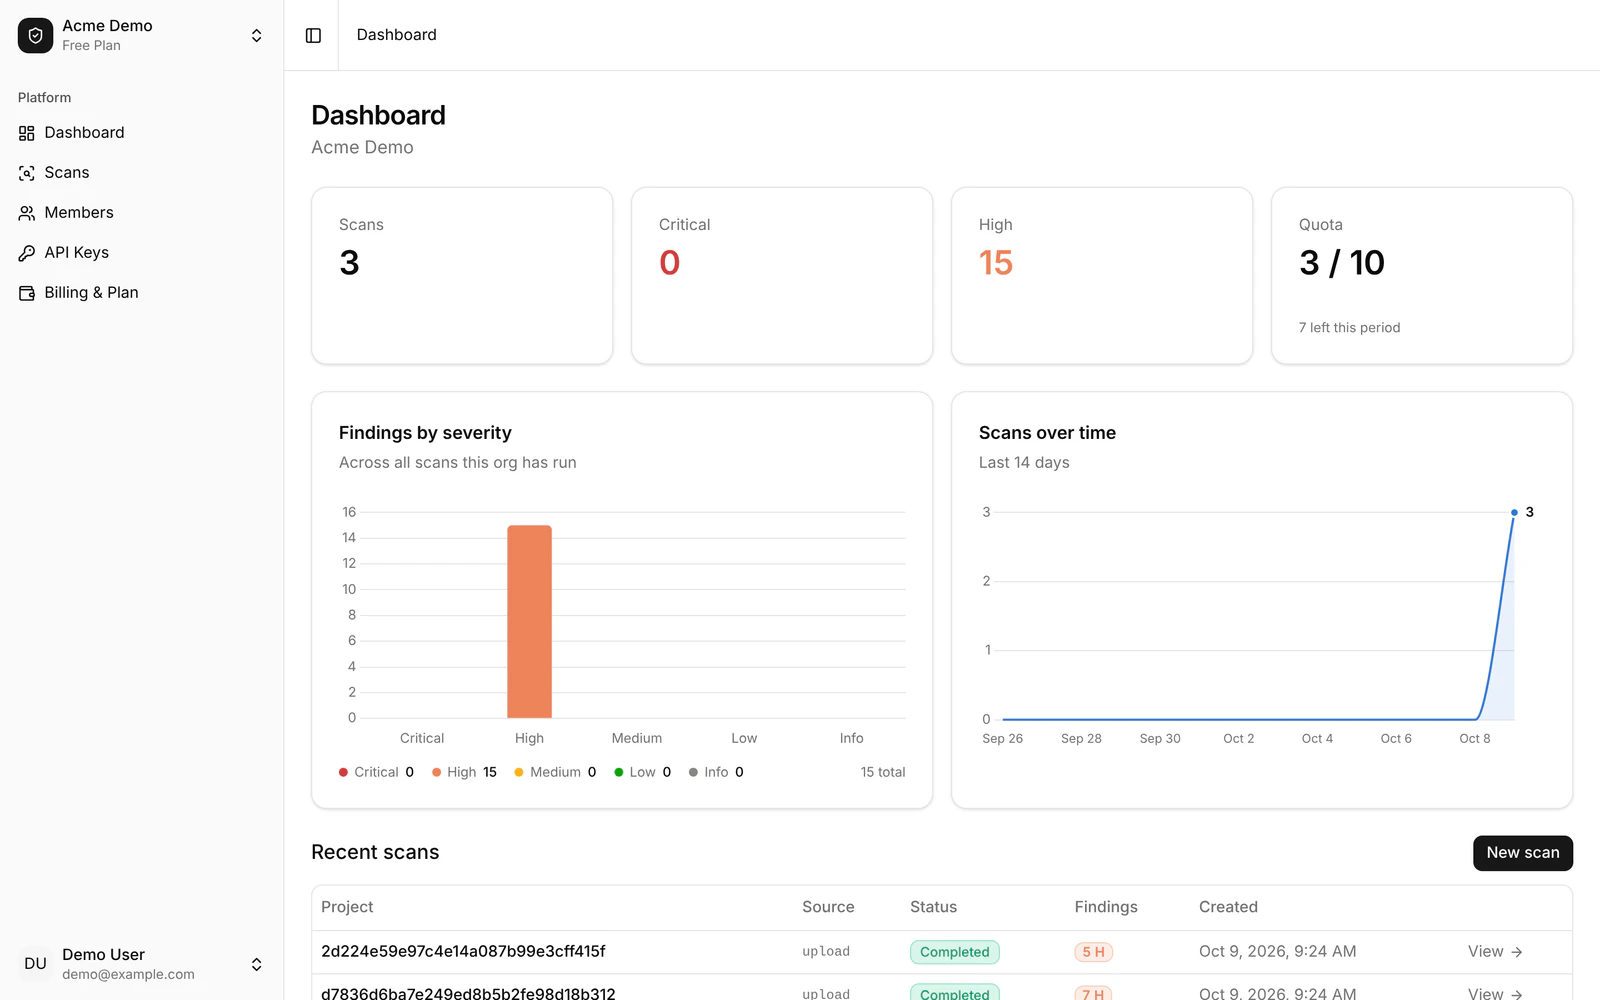
What it does
Understands the code before it judges it.
Detection knowledge lives in readable skills that the model judges, not in regular expressions alone.
Graph-based context
Builds a graph of the codebase in Python, JavaScript and TypeScript, Go, PHP, Java, Ruby and C#, and traces call chains from source to sink across files.
29 vulnerability skills
Covers the OWASP Top Ten and more: injection, access control, cryptography, secrets, SSRF and business logic.
Findings that are re-checked
A second pass re-reads the code at each finding and scores how confident it is, so a reviewer sees the evidence and the score.
Fixes, not just alerts
A finding can carry a patched snippet, shown side by side with the vulnerable code.
A scan never runs your code
A scan is static analysis: nothing it examines is executed. A hardened Docker sandbox is set up for every scan, and a hosted scan fails rather than run without one.
Built for CI
Fail a build at a severity threshold, gate only on new findings against a baseline, and upload the SARIF to code scanning.
The platform
See a scan from upload to report.
The hosted web interface: submit a repository and read the findings in the browser.
Demo data. These screens show scans of sample vulnerable apps run with a test model, so scores and wording differ from a production scan.
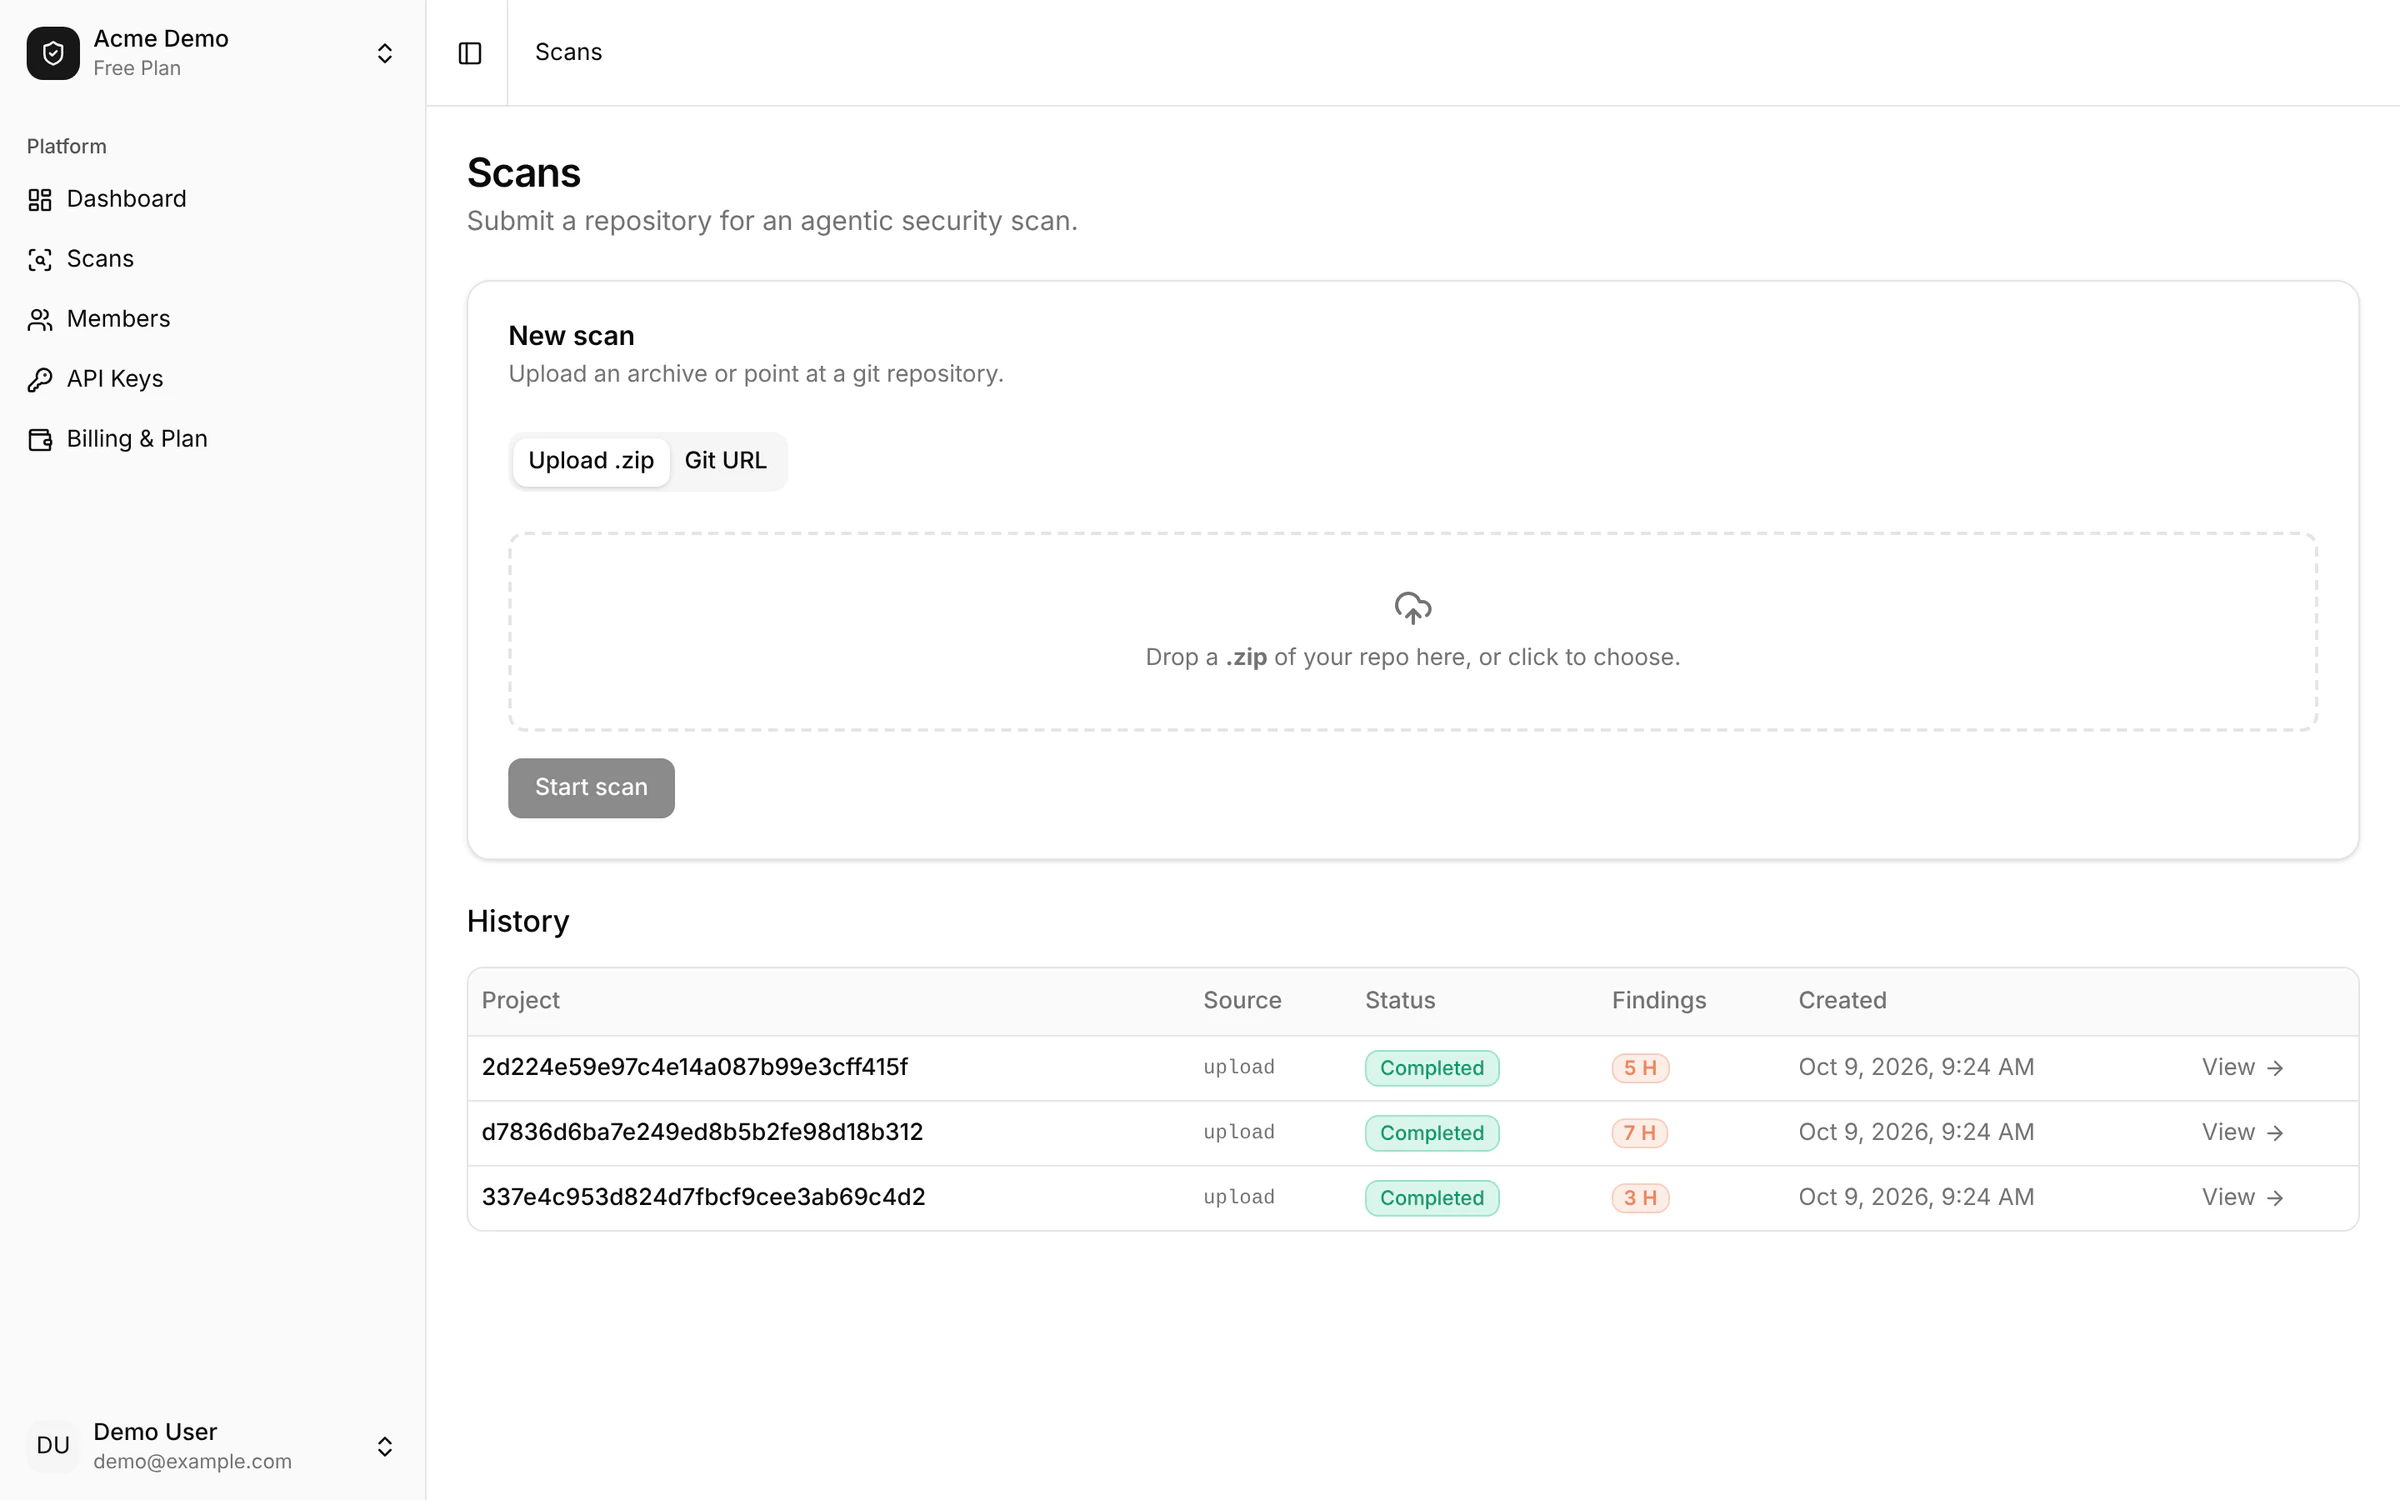
Submit a repository
Upload a zip or point at a Git repository. Each scan is queued, run and kept in the history.
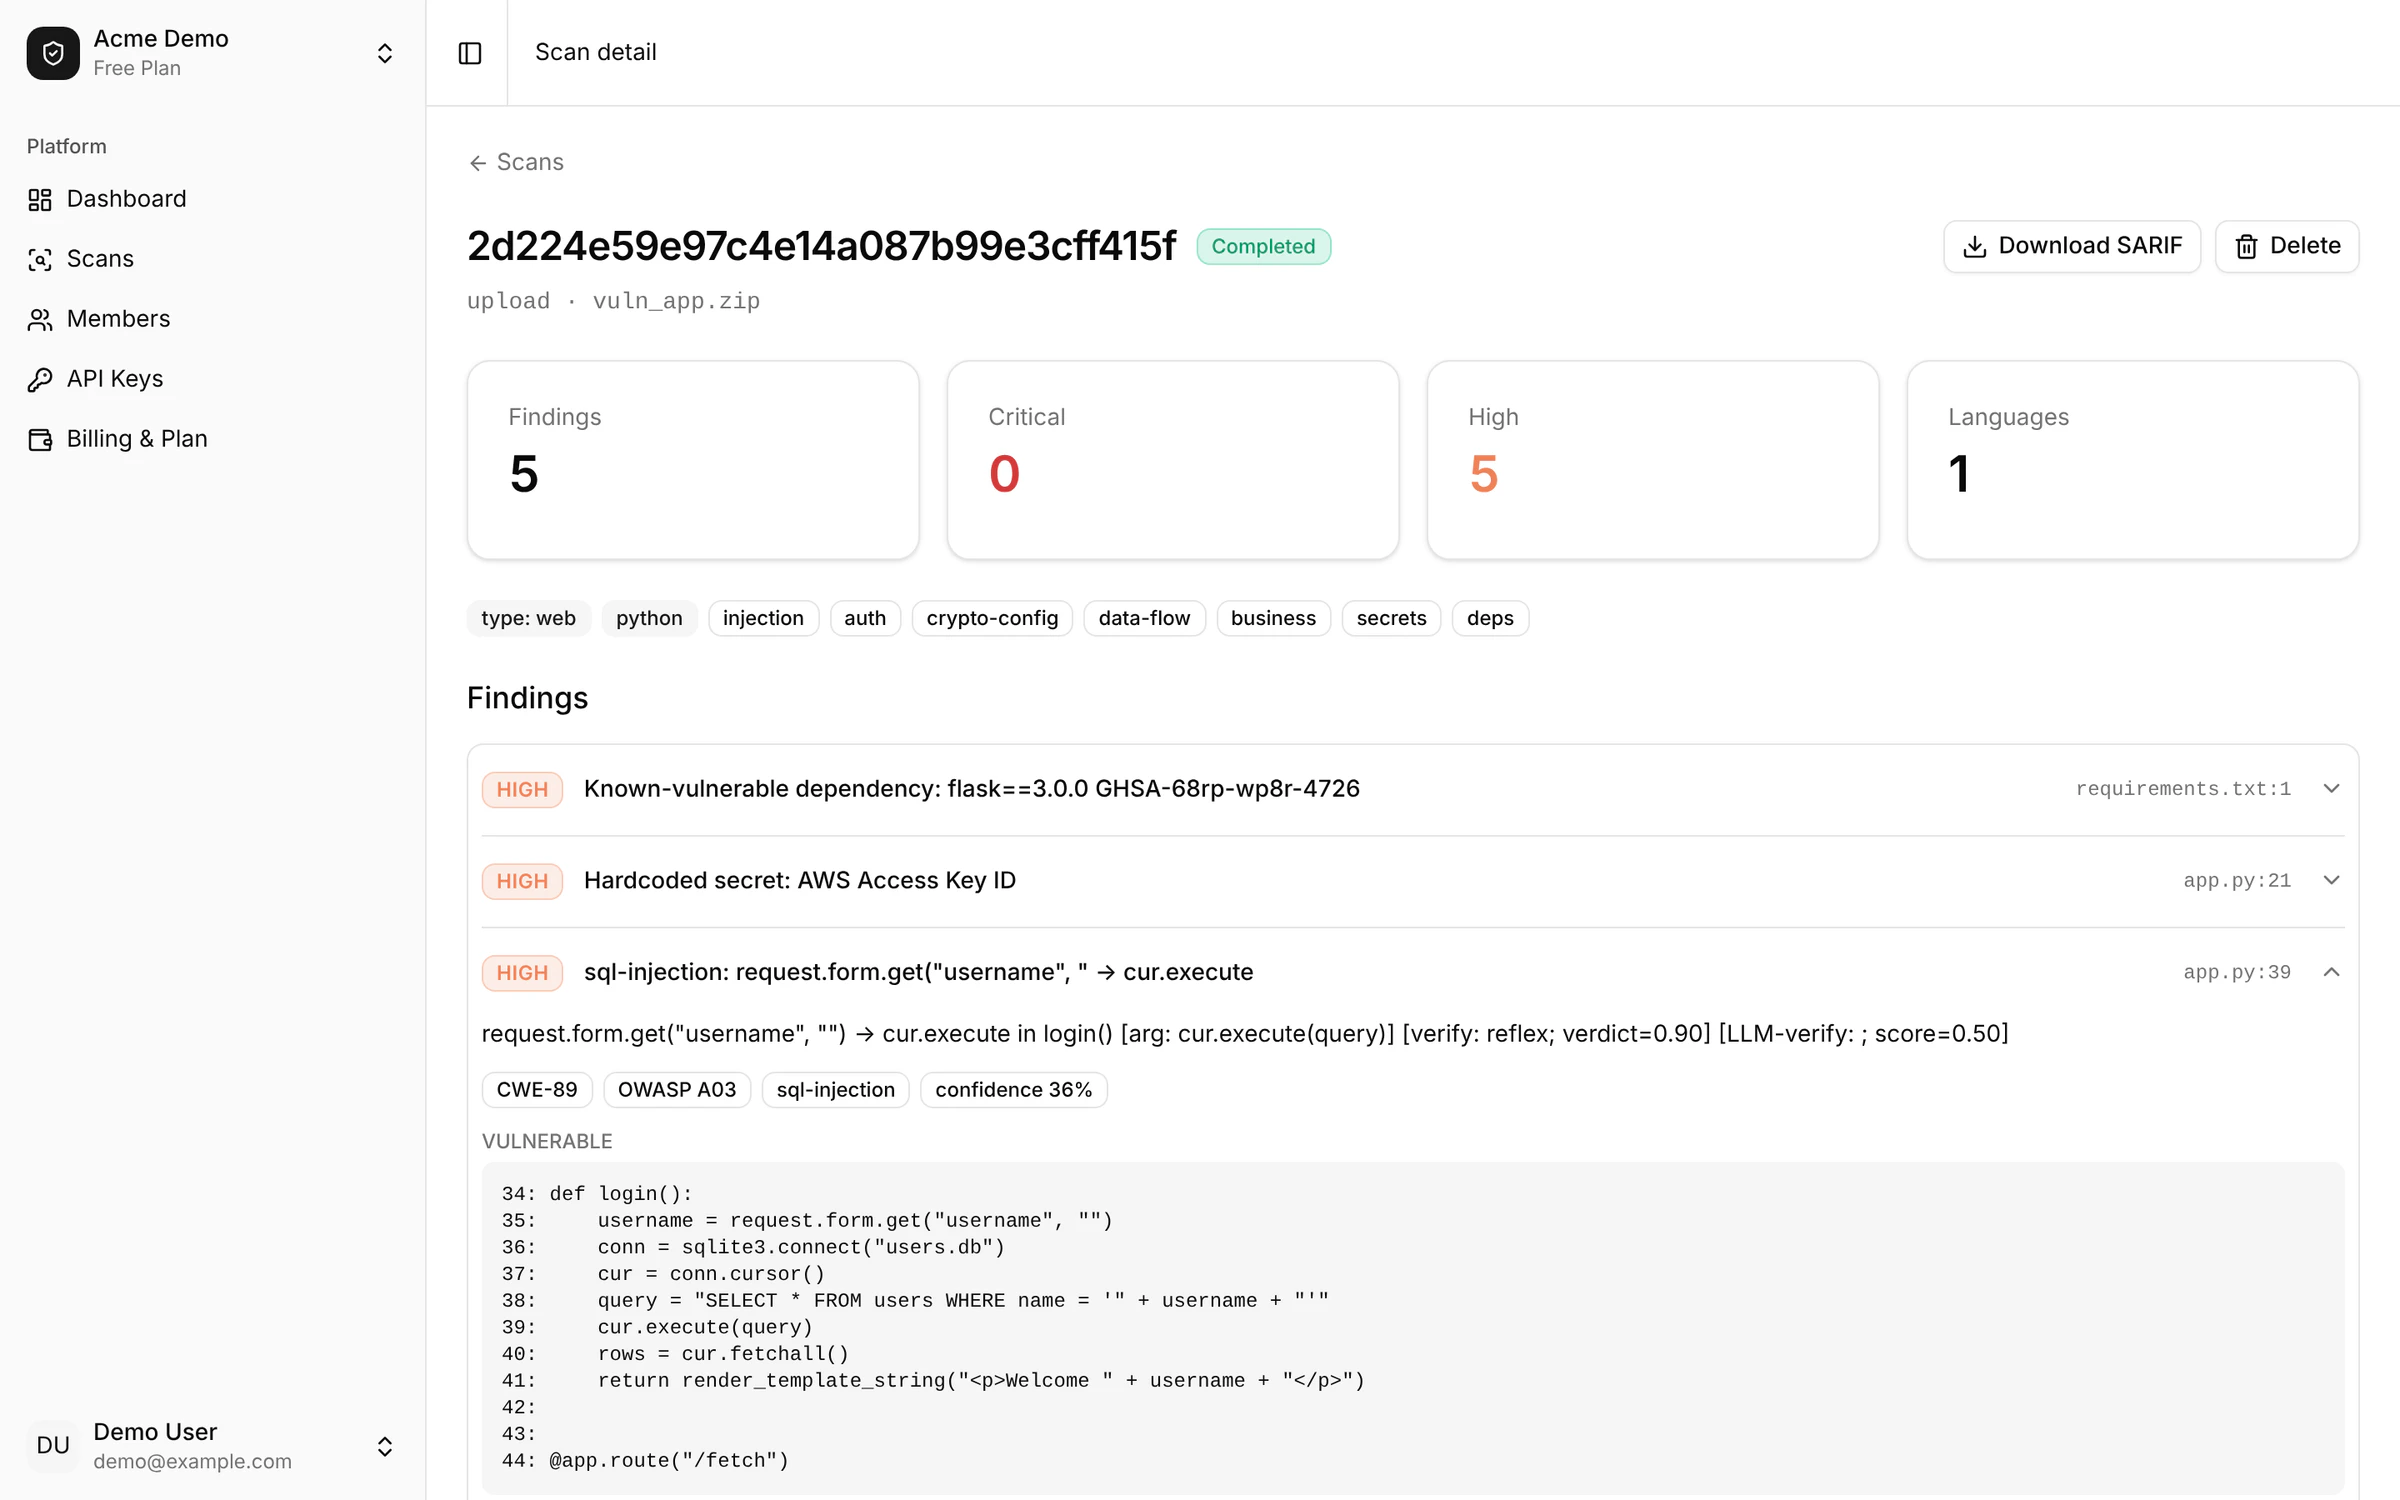
Evidence and vulnerable code
Each finding carries its CWE and OWASP category and the code around it.
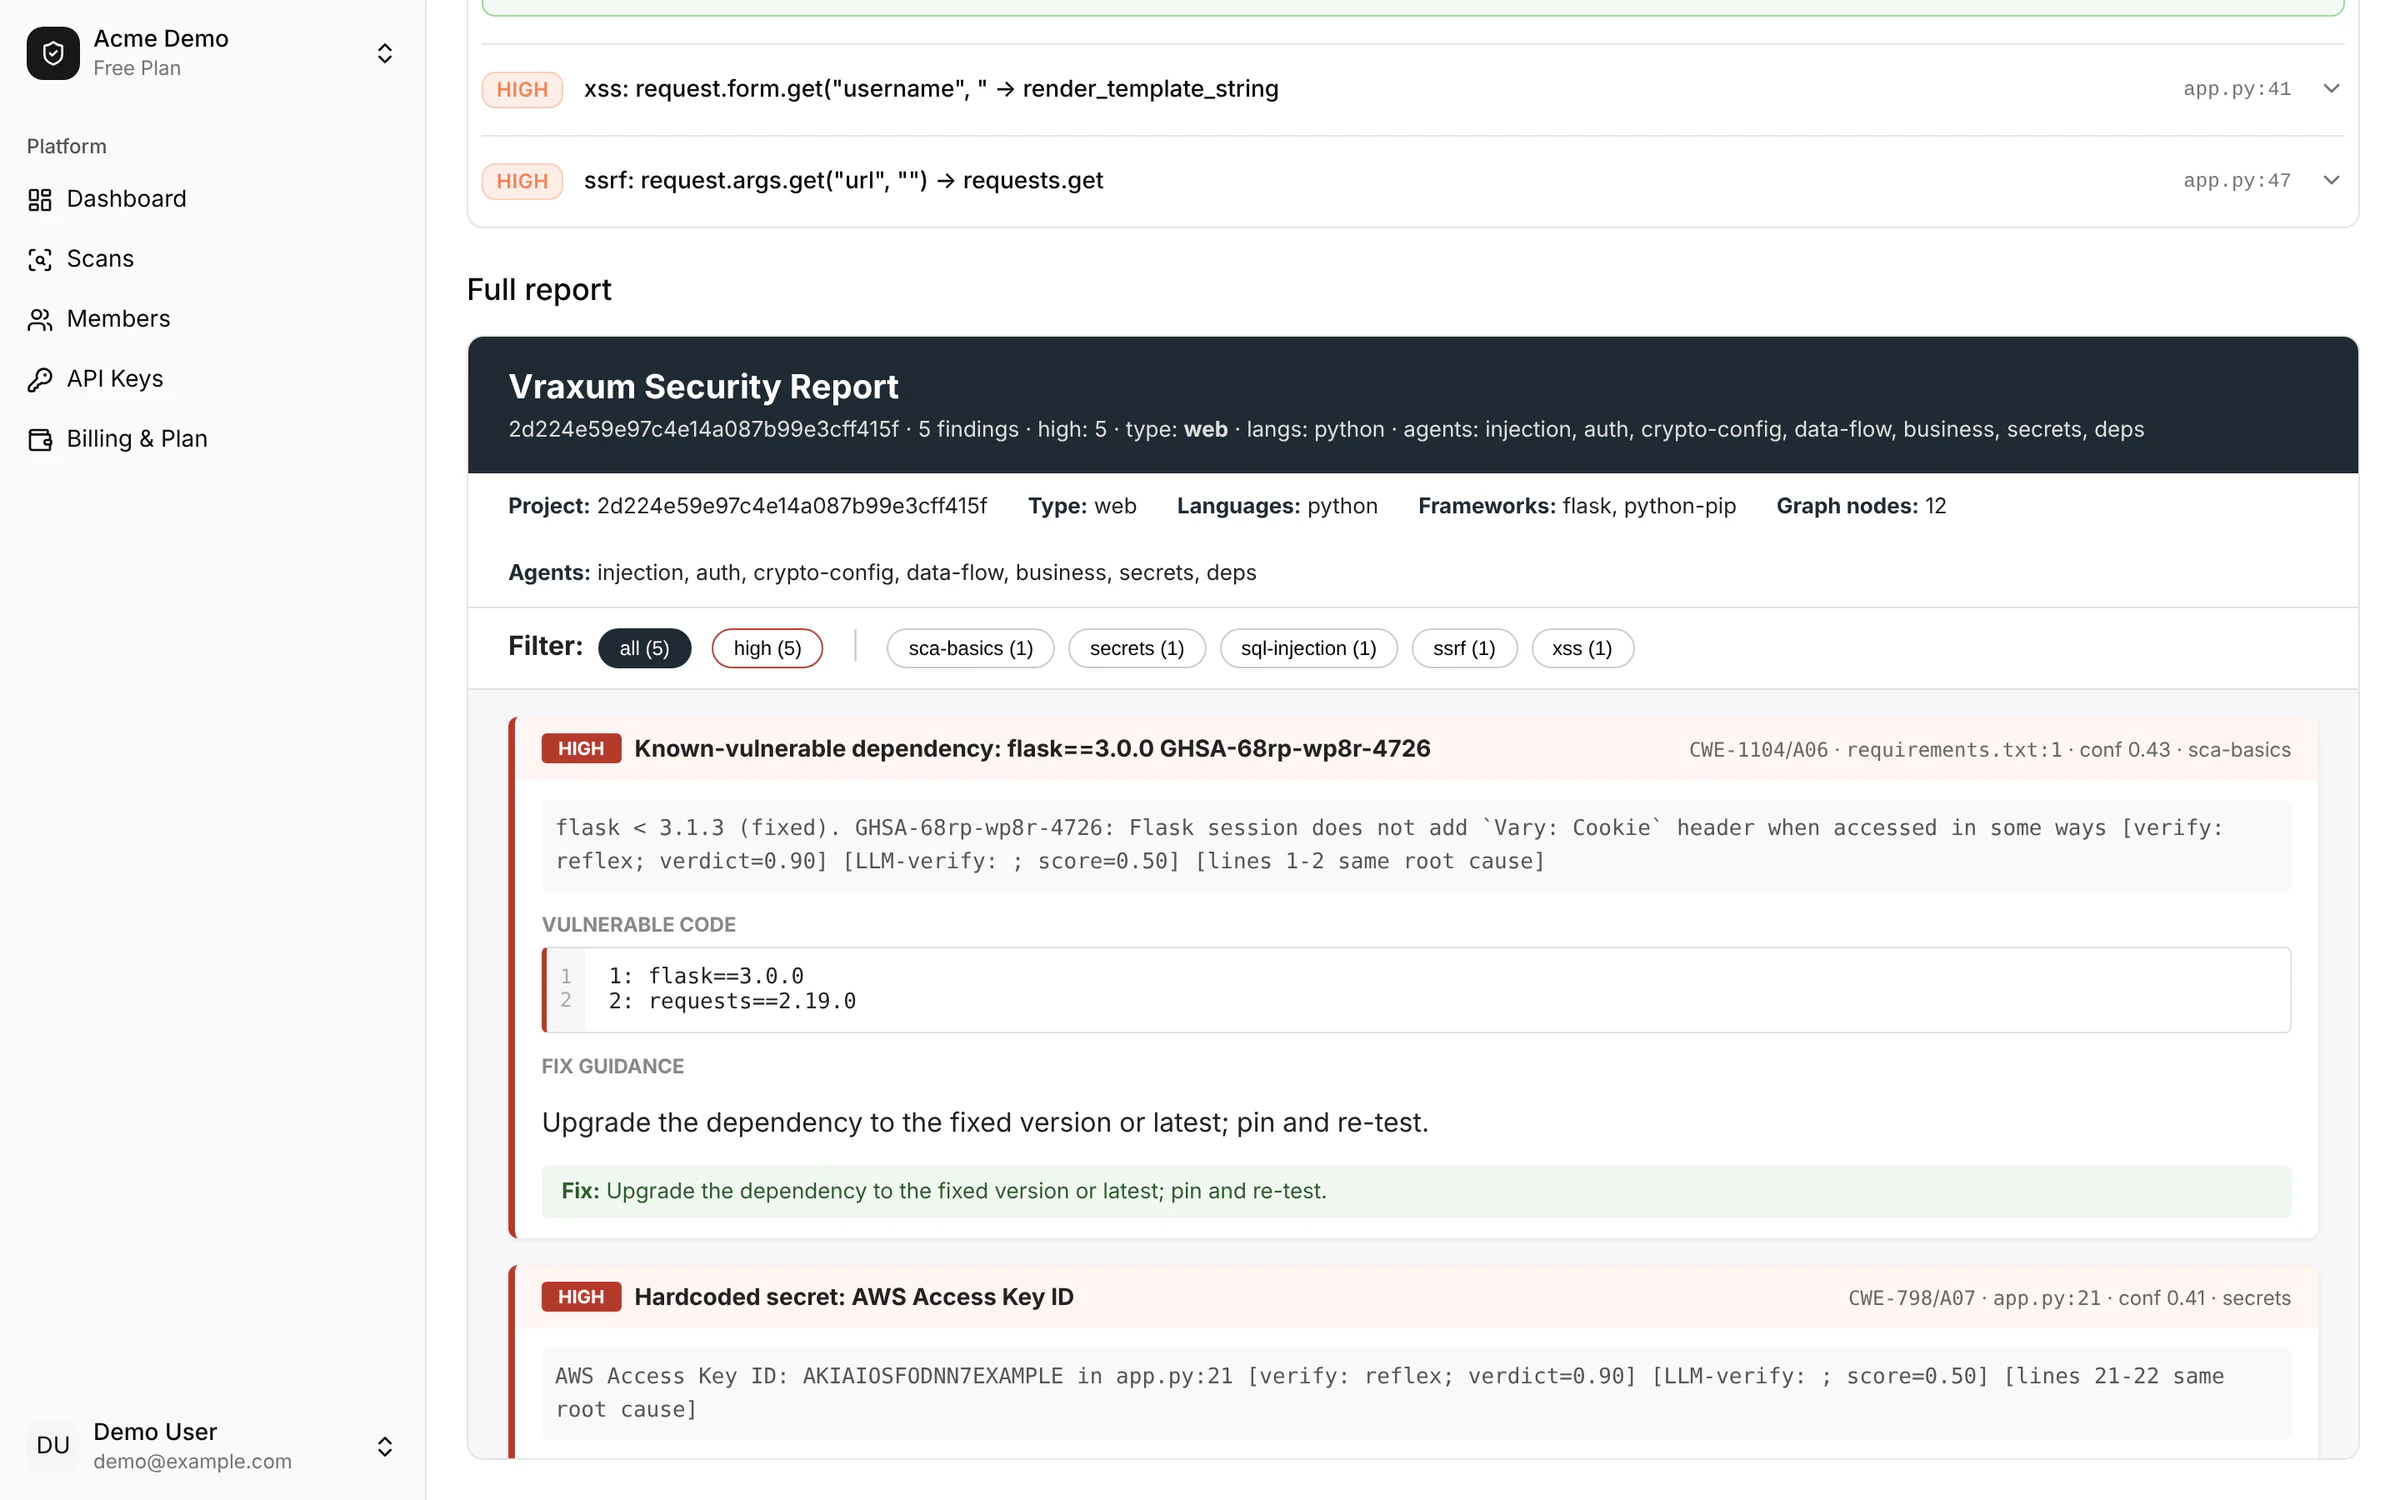
The full report
The interactive report sits in the same page, and the results download as SARIF for CI.
Want to see it on your code?
Tell us about your codebase and we will walk you through a scan.